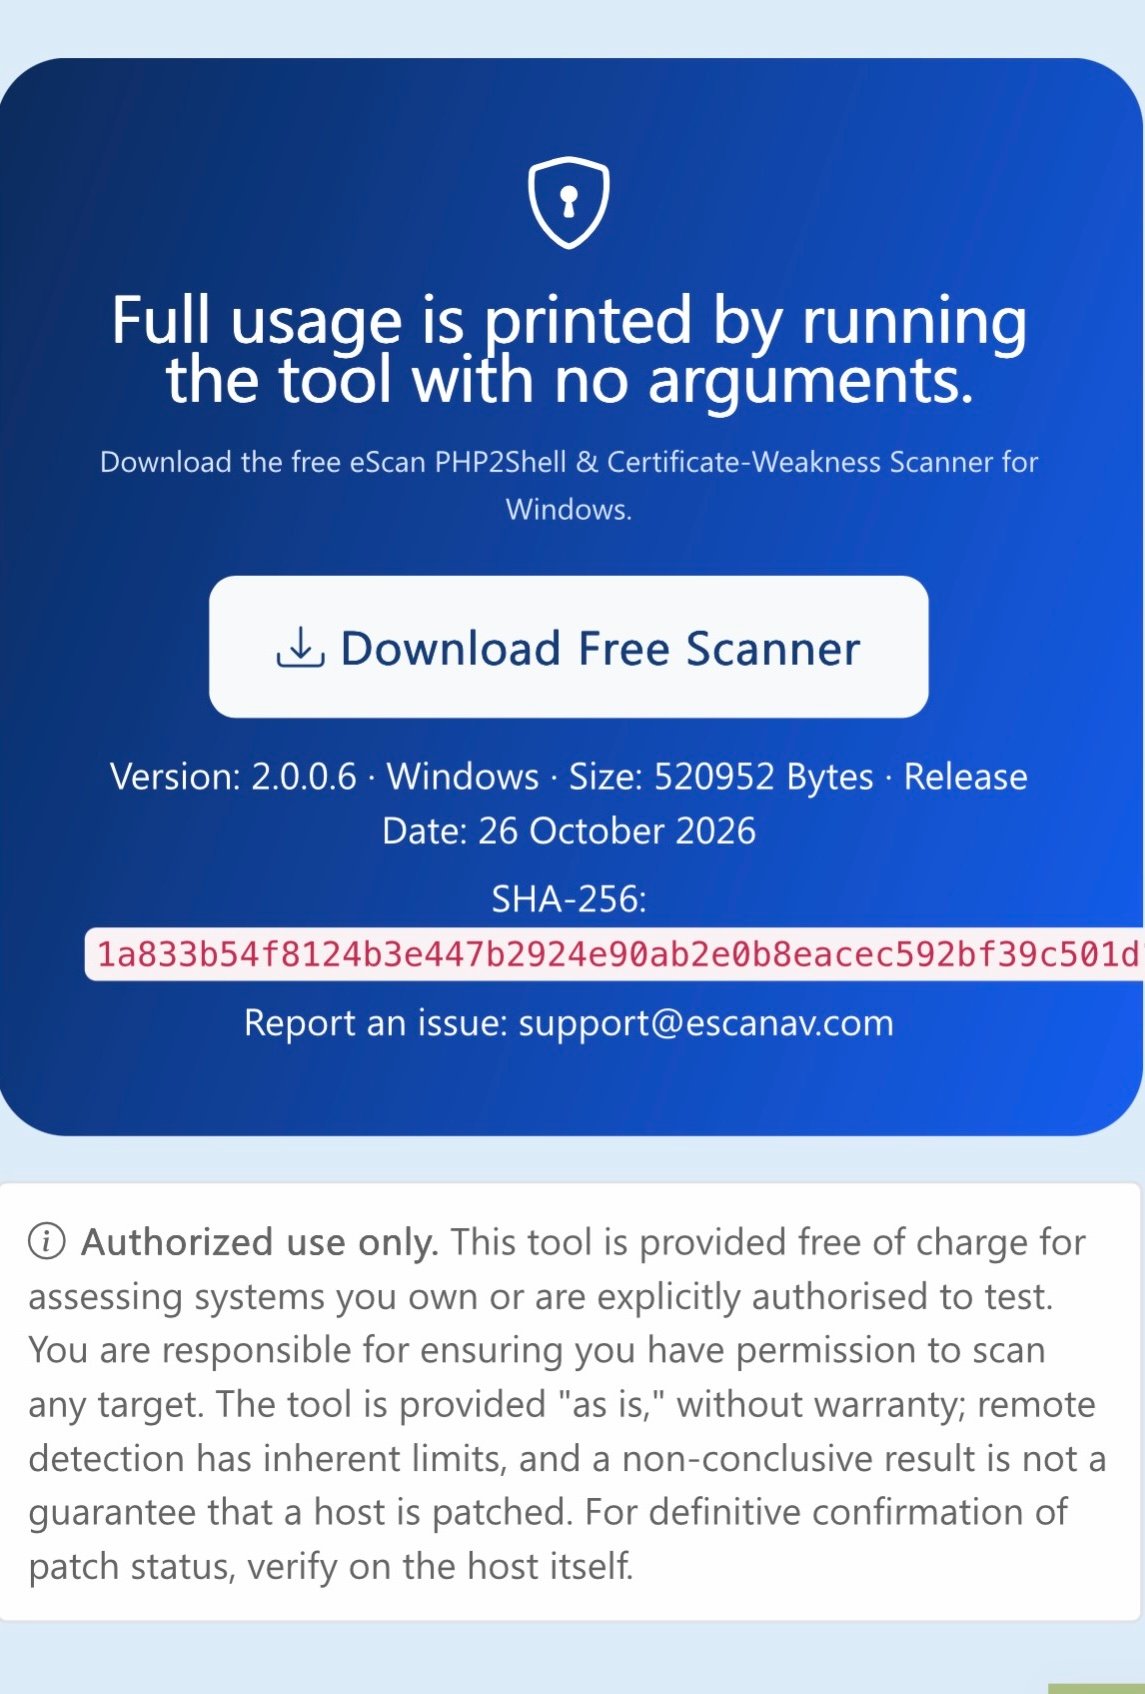
eScan, the cybersecurity brand of MicroWorld, released a free command-line scanner that lets organisations quickly identify which of their systems are exposed to two of October’s most serious security events: the PHP2Shell remote-code-execution vulnerability in PHP, and the recoverable private keys discovered in certificates issued by the certificate authority eMudhra.
PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a pair of critical flaws in PHP core - the interpreter that runs a large share of the world’s websites - rated 9.8 out of 10 on the CVSS v3.1 scale. The vulnerability allows an attacker to execute code on a server with no credentials and no user interaction. Because the flaw lives in the runtime itself rather than in any single application, every site a vulnerable server hosts is at risk. The bugs were fixed in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, while older branches receive limited or no official fixes. According to security firm Mallory, roughly 2.6 million internet-facing services were advertising a PHP version on the day the patch shipped, and close to three-quarters of them were running branches that will never receive an official release - and attackers were already probing for the flaw before the fix was public.
Days later, a second incident compounded the urgency. Researchers found that eight intermediate certificate authority keys operated by eMudhra under its emSign brand had been generated so poorly that the private keys were tiny whole numbers - one was simply the number 4 - and could be recovered by anyone in under a second (CVE-2026-111943).
Major browsers moved to withdraw trust from the affected roots, and eMudhra announced it would exit the global TLS certificate business. Because Indian government services and several banks have long relied on emSign certificates, many organisations now need a fast, reliable way to answer a question they never had to ask before: what certificate authority (CA) is my website’s trust actually anchored to, and is any certificate in that chain cryptographically weak?
eScan’s new tool answers both questions in a single sweep. Pointed at an IP address, a network range, a domain, or a file of targets, it determines each host’s exposure to PHP2Shell and inspects the full TLS certificate chain the host presents, flagging any certificate with a recoverable key and naming the issuing organisation, so that an “emSign” certificate is clearly identified as eMudhra’s. Given a domain and the relevant option, the tool also discovers its subdomains (through Certificate Transparency records) and scans each one it finds. It then prints a plain verdict, the evidence behind it, and the specific remediation for each finding.
“When a vulnerability like PHP2Shell is being exploited before the patch is even out, defenders need to find their exposed systems in hours, not weeks, and they shouldn’t have to pay for the privilege or risk knocking over the very servers they’re trying to protect,” said Govind Rammurthy, CEO and Managing Director of eScan. “We built this to be safe to run against a live estate and honest about what it can and cannot confirm. A tool that falsely reassures you is worse than no tool at all.”